Redscan Alternatives for Penetration Testing
EJN Labs is a CREST-accredited alternative to Redscan for penetration testing in the UK, and the stronger choice on six of the nine buying points compared below: a published price, a fixed quote within 24 hours, free retests until every finding is closed, free rescheduling, the report on the last day of testing and a live findings portal.
- Unlimited retesting
- Unlimited pre-retesting
- No hidden fees



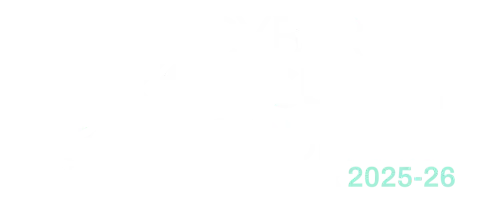
of nine buying points go to EJN Labs when the two public offers are set side by side. Both tables are below.
Redscan or EJN Labs: the Short Answer
Choose EJN Labs for a single penetration test or a yearly programme where you want the price up front, a fixed quote within 24 hours, free retests until every finding is closed and the report on the last day of testing.
Choose EJN Labs if you also need Cyber Essentials or Cyber Essentials Plus. EJN Labs is an IASME Certification Body and issues the certificate itself.
Choose Redscan if you want managed detection and response or incident response from the same group as your testing.
BUYING POINTS
Redscan vs EJN Labs: Pricing, Retests and Report Delivery
EJN Labs is stronger on six of the nine points: published pricing, quote turnaround, retests, rescheduling, report delivery and findings. On each of those EJN Labs commits to a figure, a date or a live portal in writing; Redscan’s pages state day-based pricing with no figures, an optional retest and a written report after the engagement. Redscan does not appear on the CREST Marketplace under its own name; the listing that covers it is Kroll’s. Redscan is stronger where a requirement names CREST-accredited incident response or a security operations centre. For a buyer who needs a CREST-accredited penetration test delivered at a known price, on a known date, with the fixes confirmed at no extra cost, EJN Labs is the better fit.
| What to check | Redscan | EJN Labs | Stronger on this point |
|---|---|---|---|
| CREST penetration testing accreditation | Verified: CREST Marketplace listing, under Kroll | Verified: CREST Marketplace listing | Even: Redscan is listed under Kroll |
| Published pricing | Priced by the number of days needed to achieve an agreed objective; no price figures on its public pages | A starting price for every service below and a day rate of £1,100 to £1,400 on the pricing page; every engagement is a fixed price for a defined scope | EJN Labs |
| Quote turnaround | Not stated on its public pages | Fixed quote within 24 hours of a 30-minute scoping call, through the quote form | EJN Labs |
| Retests | Optional retesting exercise to validate the applied fix, listed under agile penetration testing | Free until every finding is closed, included in the price; by EJN Labs’ own figures, up to 35% saved against paying for retesting separately | EJN Labs |
| Rescheduling and cancellation | Not stated on its public pages | Free rescheduling before or after kick-off; no callout, cancellation or out-of-hours fees | EJN Labs |
| Report delivery | Custom written report after each engagement, then a telephone debrief | On the last day of testing, with a signed letter of attestation; see the sample report | EJN Labs |
| Findings | Manually-written report with an executive summary and recommendations on addressing risks | Live client portal with findings posted as they are confirmed, a CVSS score on every finding and a walkthrough call | EJN Labs |
| Testers | London based team of ethical hackers; red team of CREST accredited ethical hackers | UK-based, CREST-certified penetration testers on every engagement; SC-cleared testers available | Even |
| Certifications | CREST member, per its penetration testing page; ISO27001 company certification, shown on the Kroll CREST listing | ISO 27001, ISO 9001, Cyber Essentials and Cyber Essentials Plus; IASME Certification Body for Cyber Essentials and Cyber Essentials Plus | Redscan (Kroll) for incident response and SOC; EJN Labs for Cyber Essentials |
Redscan details come from its own public pages, 29 October 2026. Where a cell says not stated or not listed, ask Redscan for the answer for your scope and set it against the EJN Labs column.
SERVICES COMPARED
Redscan vs EJN Labs: Services Compared
EJN Labs covers all twelve services and shows a starting price for each one on its pricing page. Redscan covers ten and shows no price figures: AI and LLM penetration testing and Cyber Essentials certification are not listed on its public pages. Redscan also offers agile penetration testing, breach and attack simulation and scenario-based testing next to its managed detection and response line. If you need an AI test or Cyber Essentials alongside the penetration test, EJN Labs can cover it under one supplier.
| Service | Redscan | EJN Labs |
|---|---|---|
| Web application penetration testing | Yes. Web application penetration testing services proactively assess applications to identify vulnerabilities. No price shown | Yes, from £5,000. Manual testing of the OWASP Top 10, business logic, access control and authentication, with every finding mapped to OWASP ASVS |
| API penetration testing | Yes. Penetration tests assess backend application logic and software and API source code. No price shown | Yes, from £4,000. All ten OWASP API Security Top 10 categories on every engagement, across REST, GraphQL, JWT and OAuth |
| Mobile application penetration testing | Yes. Mobile security testing to protect devices and apps against the latest cyber threats. No price shown | Yes, from £4,500. iOS and Android in one engagement, with the APIs behind them, tested against OWASP MASVS |
| External infrastructure penetration testing | Yes. External penetration testing is undertaken remotely by ethical hackers. No price shown | Yes, from £3,500. Attack-surface discovery and manual exploitation of every reachable service, aligned to PTES and NIST SP 800-115 |
| Internal network penetration testing | Yes. An internal network pen test gauges what an attacker could achieve with initial access to a network. No price shown | Yes, from £1,200. Assumed-breach testing of lateral movement, privilege escalation and Active Directory by hand, mapped to MITRE ATT&CK |
| Cloud security review (AWS, Azure, GCP) | Yes. Custom assessments to protect your cloud environments from cyber threats. No price shown | Yes, from £4,500. AWS, Azure and GCP configuration reviews against the CIS Benchmarks, with hands-on exploitation |
| Red teaming | Yes. Simulated cyber-attack on detection and response; scenario-based operations over 11-18 days. No price shown | Yes, from £15,000. Intelligence-led adversary simulation mapped to MITRE ATT&CK, with a detection review alongside your blue team |
| Phishing and social engineering | Yes. Customised real-life phishing exercises designed around your organisation. No price shown | Yes, from £3,000. Email phishing, vishing, smishing, MFA fatigue and OAuth phishing, reported with click and credential-capture rates |
| Secure code review | Yes. Application and API security review: tests assess software and API source code. No price shown | Yes, from £3,500. Manual review with SAST across Java, Python, JavaScript, TypeScript, Go and C#, mapped to OWASP ASVS and the CWE Top 25 |
| AI and LLM penetration testing | Not listed on its public pages | Yes, from £6,000. Manual exploitation of prompt injection, jailbreaks, training-data poisoning and model theft, against the OWASP Top 10 for LLM Applications |
| Vulnerability assessment and penetration testing (VAPT) | Yes. VAPT combines vulnerability assessment and penetration testing for a thorough analysis. No price shown | Yes, from £4,000. Automated scanning and manual exploitation in one engagement and one report |
| Cyber Essentials and Cyber Essentials Plus certification | Not listed on its public pages | Yes. IASME Certification Body that assesses and issues the certificate, from £400 and £1,200 |
“I would highly recommend EJN Labs to any organisation seeking reliable, detailed, and well-managed penetration testing services, particularly for government or enterprise-level projects.”
“There wasn’t another company we could find that could deliver what we needed in the timeframe we needed. The client loved it, and we got instant ROI from the engagement.”
SECOND QUOTE
How to Run a Second Quote
Write the Scope
One page: the assets, user roles, environments and the dates you can offer. Send the same page to every provider so the prices compare like for like.
Ask for a Fixed Price
Ask each provider for a fixed price for that scope and the date the report arrives. EJN Labs replies within 24 hours of a 30-minute scoping call.
Ask About Retests
Ask what a retest costs and how long it stays available. EJN Labs retests for free until every finding is closed.
Read a Sample Report
Ask for a sample report before you sign. EJN Labs publishes its sample penetration test report.
CREDENTIALS
Verified Accreditations Auditors Accept
Every credential below is independently verifiable. UK procurement teams, FCA supervisors, ISO 27001 / SOC 2 auditors, and cyber insurance underwriters all recognise these standards.




GET YOUR QUOTE
Get a second CREST pen test quote in 24 hours
A fixed-price quote back in one business day, from a named CREST assessor. No sales pipeline, no chasing.
- CREST and IASME accredited. Testing your auditors and clients already recognise.
- Fast-track testing within 24 hours where required. Free retest of every fix included.
- Live findings via your client portal, not a four-week PDF.
- Fixed price from £3,500 for a single-role, single-app scope, agreed up front. Most engagements run £5,000 and up. No day-rate surprises.
 Dan WilcocksonFounder, Cellori
Under NDA Further named references available on a scoping call.
- We reply within one business day with a fixed-price quote from a named CREST assessor.
- You approve the scope and we book a start date, usually within 24 hours.
- Live findings land in your client portal as we test, with a free retest of every fix.
Get your fixed pen test quote in 24 hours
Quote request received
We will reply within one business day with your fixed-price quote from a named CREST assessor.
Your data stays with us. No newsletter signup.
or book a 20-min scoping call first
We reply within one business day. Your data stays with us. No newsletter signup.
PRICING
Published Prices on Every Service
Every EJN Labs service has a starting price on the pricing page, from £1,200 to £15,000. The web application tiers below show how a fixed price is built.
Depends on app complexity
Single user role, basic CRUD application, marketing website with auth. Around 5 working days from kickoff to report.
Get a fixed quoteDepends on app complexity
Multi-role SaaS, business application with payment integration. Around 8 to 12 working days from kickoff to report.
Get a fixed quoteDepends on app complexity
Multi-tenant platform, complex authorisation matrix, integration-heavy applications. Around 15 to 20 working days from kickoff to report.
Get a fixed quoteWHY EJN LABS
What You Get From an EJN Labs Penetration Test
Six concrete differentiators competitors don’t all match.
CREST-Certified Testers, Verifiable
Every test by a CREST-certified pen tester (CRT, CCT APP, CCT INF where applicable). Verify our company status at crest-approved.org.
24-Hour Startup, Where Required
From signed scope to active testing in a single business day for incident response, audit deadlines, or regulator-driven timelines.
Live Findings, Not 4-Week PDFs
Critical issues reported during testing through your client portal. Your team remediates while testing continues.
Audit-Ready Reports
Executive summary plus full technical report with CVSS scores and explicit framework mappings (ISO 27001, SOC 2, PCI DSS, FCA SYSC).
Free Retests, Standard
Verify remediation of every finding before close-out. Letter of attestation for audit submission included. Most competitors charge £1,500-£3,000 per retest.
UK-Based CREST Testers
Every engagement performed by vetted, UK-based CREST-certified testers, matched to your needs, security clearance, and compliance scope.
FAQ
Frequently Asked
Is EJN Labs a good alternative to Redscan?
Yes. EJN Labs holds its own CREST Penetration Testing accreditation, publishes a starting price for every service, gives a fixed quote within 24 hours, includes free retests until every finding is closed and delivers the report on the last day of testing. Redscan’s public pages give no price figures or quote time, and its retest is optional.
Which is better for a single penetration test, Redscan or EJN Labs?
For a single CREST-accredited test of an application, an API, a cloud account or a network, EJN Labs is the better fit, because the price, the quote date, the retest terms and the report date are all stated up front. Redscan is the better fit where you want managed detection and response or incident response from the same group.
When is Redscan the better choice?
Redscan lists a wide menu on its services page: web application, mobile, cloud and network testing, agile penetration testing, red teaming, breach and attack simulation and scenario-based testing, alongside managed detection and response and incident response. Its penetration testing page says the work is done by a red team of CREST accredited ethical hackers and that Redscan is a member of CREST. Its red teaming page says a full end-to-end engagement is typically performed over one to two months, with narrower scenario-based operations over 11-18 days. A buyer who wants testing, detection and response from one group will find that combination on Redscan’s pages. Kroll’s CREST Marketplace listing shows Incident Response, Penetration Testing and Security Operations Centre among its accredited disciplines. Where a requirement names CREST-accredited incident response or a CREST-accredited security operations centre, use a provider accredited for it, and Kroll’s listing shows both. Where it asks for a CREST-accredited penetration test, EJN Labs meets it, with the price, the quote date and the retest terms stated up front.
Is Redscan CREST-accredited?
There is no listing for Redscan on the CREST Marketplace. The listing that covers it is Kroll’s, which shows Incident Response, Penetration Testing and Security Operations Centre as accredited disciplines, a United States of America headquarters and an ISO27001 company certification. Redscan’s own penetration testing page says it is a member of CREST. Read the Kroll listing on the CREST Marketplace and confirm with the supplier which legal entity will deliver your test.
Does Redscan publish its penetration testing prices?
No. We could not find price figures on its public pages. Its penetration testing page says the cost of a pentest is based on the number of days its ethical hackers need to achieve an agreed objective, and that a quotation follows a pre-evaluation questionnaire. Ask for a fixed price for your scope on a first call.
How much does EJN Labs charge for a penetration test?
EJN Labs publishes its prices. A web application test starts from £5,000, an API test from £4,000, a mobile application test from £4,500, an external infrastructure test from £3,500, an internal network test from £1,200, a phishing assessment from £3,000, a cloud security review from £4,500 and a focused red team from £15,000, all on the pricing page. The day rate is £1,100 to £1,400, every engagement is a fixed price for a defined scope, and retests, rescheduling and the letter of attestation are included.
What other Redscan alternatives are there?
EJN Labs is compared in full on this page. We also compare EJN Labs with NCC Group, LRQA, Precursor Security, Pen Test Partners, OnSecurity, Sencode, Bridewell, CyberLab, DeepStrike, and every comparison is listed on the alternatives page.
20+ CREST-accredited testing services in one place
Web, mobile, API, cloud, AI, infrastructure, red team. Pick the test that fits your environment.
Get your second quote
Send us the scope you gave your current provider. You get a fixed price within 24 hours of a 30-minute scoping call.


